
godot_reverse_engineering
Table of Contents
De-compiling encrypted Godot games
de-compile using https://github.com/GDRETools/gdsdecomp
Instructions
- load the binary you want to decompile in ghidra
- click search→for instruction patterns
- click enter bytes manually
- input the following hex after changing it to hex mode
48 85 c0
0f 84 00 00 00 00
48 83 78 00 20
0f 85 00 00 00 00
- click apply
- click the O(mask all operands)
- uncheck the 0x20 in the CMP
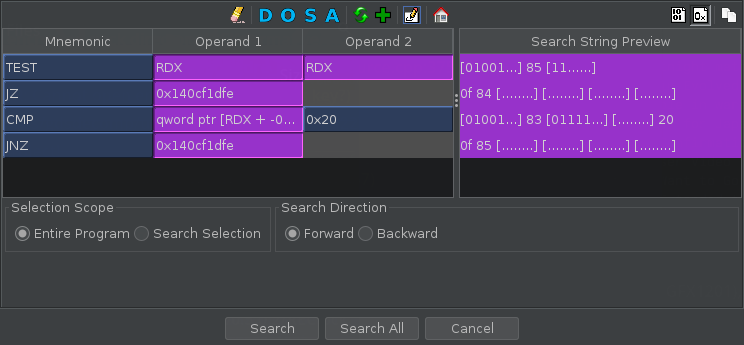
- click find all
- click the only result (if this changes in the future just know that if you decompile the function it should have “p_key.size() != 32” in an error code.)
- take note of which register is being tested
- load the game in a debugger and set a break point for the test address
- read 32 bits from the pointer at the address being tested
linux debug steps for windows game:
winedbg your_game.exe

Wine-dbg>break *0x140cf1d67 (example address for REC)
Breakpoint 1 at 0x00000140cf1d67 rec+0xcf1d67
Wine-dbg>cont
Stopped on breakpoint 1 at 0x00000140cf1d67 rec+0xcf1d67
Wine-dbg>disassemble
0x00000140cf1d67 rec+0xcf1d67: testq %rdx, %rdx (note the rdx register being tested)
...(rest of the disassemble)
Wine-dbg>x /32b $rdx (read 32 bytes out of the address contained in rdx)
0x007f9bde7c7ab0:  5e 0e 4d e3 a9 01 9f 0b 92 a8 f9 35 cf c4 4e 7a
0x007f9bde7c7ac0:  4b 5f 3a 14 20 1b 47 7d f8 96 5d ba 67 18 97 39
windows:
todo
Examples
Anomalous coffee machine
url: https://horubrain.itch.io/anomalous-coffee-machine
godot version: 3.5.4.rc.custom_build.470ef4d63
commit date: May 11, 2024 (main line godot)
script_encryption_key(linux):
957aba86a4f9009237ccc763f22c8bfda51c9794f0db7749360591987c0dea49
REC
url: https://moondev64.itch.io/rec
godot version: 4.4.1
key extracted from version: 0.5.0.2
encryption key(windows):
5e0e4de3a9019f0b92a8f935cfc44e7a4b5f3a14201b477df8965dba67189739
godot_reverse_engineering.txt · Last modified: by winwinner